Onboarding done in 24 hours
Kick-off, access, tracking and the first audit completed within 24 hours, so your CSPM platform starts winning search on day one.
See the 24h onboarding →
Cloud security posture management is a crowded, technical, and high-stakes category. Buyers are CISOs, cloud architects, and DevSecOps leads who run exhaustive research cycles before they ever book a demo. If your CSPM platform is not ranking for the queries these buyers type into Google, your CAC climbs and your pipeline stalls.
Novalab builds organic search programs for CSPM SaaS companies that need qualified traffic, not vanity metrics. A SaaS SEO agency that treats cloud architects like generic B2B buyers will keep shipping the wrong misconfiguration and compliance keywords. We map your content to how security buyers actually research and compare tools.
Kick-off, access, tracking and the first audit completed within 24 hours, so your CSPM platform starts winning search on day one.
See the 24h onboarding →We cover misconfiguration risks, compliance mandates like SOC 2, PCI-DSS and CIS Benchmarks, and bottom-of-funnel alternative searches, so each query reaches the right page.
See the approach →CPC rates for terms like "cloud security posture management" regularly exceed $50. A ranking comparison page or compliance guide keeps driving demos without ongoing spend.
See how →Most SEO agencies treat cloud security like any other software vertical. They produce shallow blog posts, chase broad keywords, and wonder why MQLs never convert. CSPM is different, because buyers already know the problem.
They are evaluating Wiz, Orca, Lacework, and Palo Alto Prisma before they land on your site. Generic content does not make that shortlist. Our SEO for attack surface management SaaS work follows the same external-exposure research path when a buyer is comparing ASM to cloud posture tooling.
We also audit your existing content architecture. Many CSPM companies have product pages that speak to engineers but ignore the economic buyer. We close that gap so your site converts across the full buying committee.
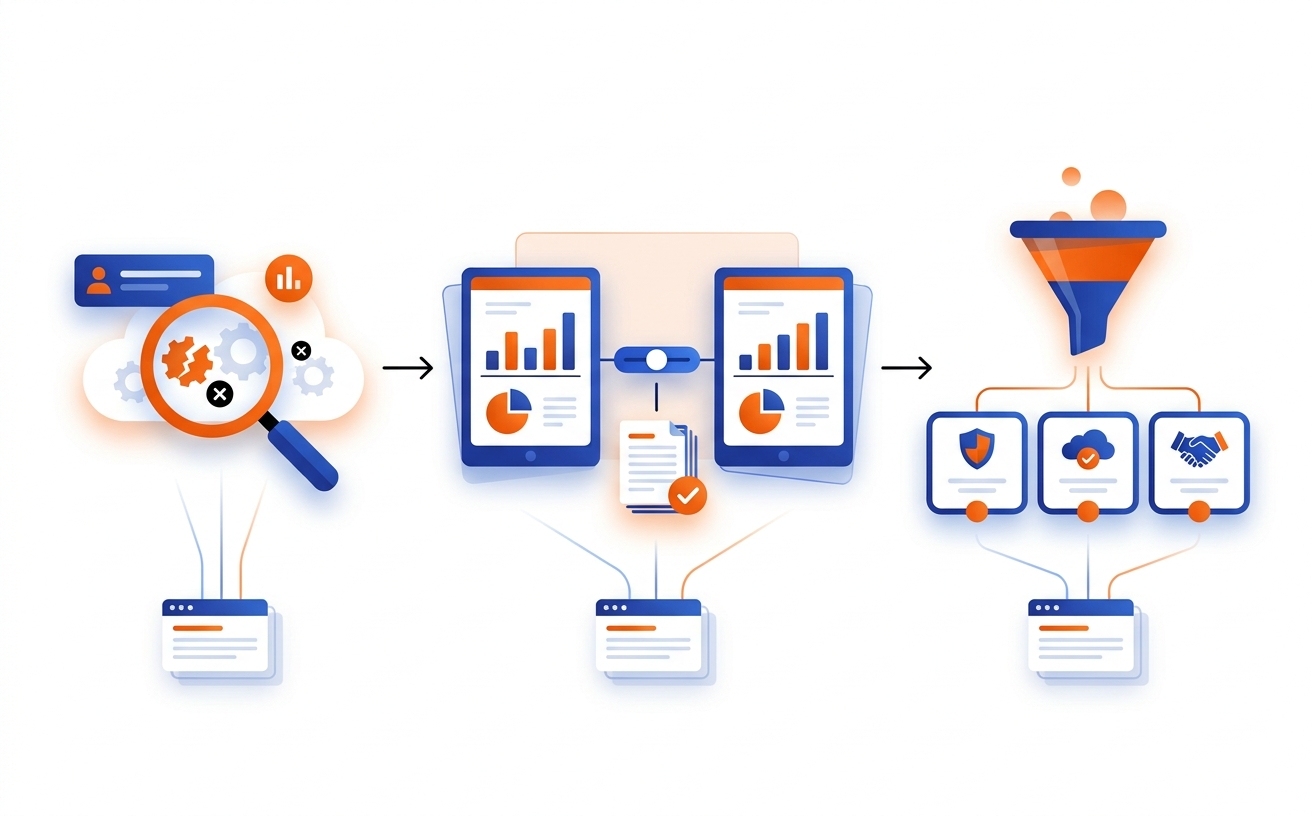
We start by mapping your keyword universe to real buying stages. That runs from awareness around AWS, Azure and GCP misconfigurations, through compliance frameworks, to high-intent comparison and alternative queries. Every piece of content is written to match the sophistication of a security-focused reader.
Paid acquisition in cybersecurity is expensive. Organic search compounds, which improves your CAC payback period and makes MRR growth more predictable. For broader security tooling, our SEO for cybersecurity SaaS program follows the same operations content path.
Novalab tracks every engagement against pipeline contribution, not just rankings. We connect organic traffic data to your CRM to show which content drives trial sign-ups and which pages assist enterprise demo requests. You see the revenue impact, not just search impressions.
CSPM buyers do significant self-directed research before they fill out a form. Studies consistently show that B2B security buyers complete more than half their evaluation before talking to sales. Ranking in that research phase means you shape the buyer’s criteria before competitors know they exist.
That research often crosses into adjacent topics. A CISO weighing posture tooling may also be reading about vulnerability management SaaS and how exposure gets prioritized, or about governance and SOC 2 and privacy compliance alongside cloud posture. We build content that meets the buyer on each of those paths.
The result is a durable pipeline advantage. Comparison pages, compliance guides and cloud provider pages keep working long after they are published, and they reach buyers who are already close to a decision.
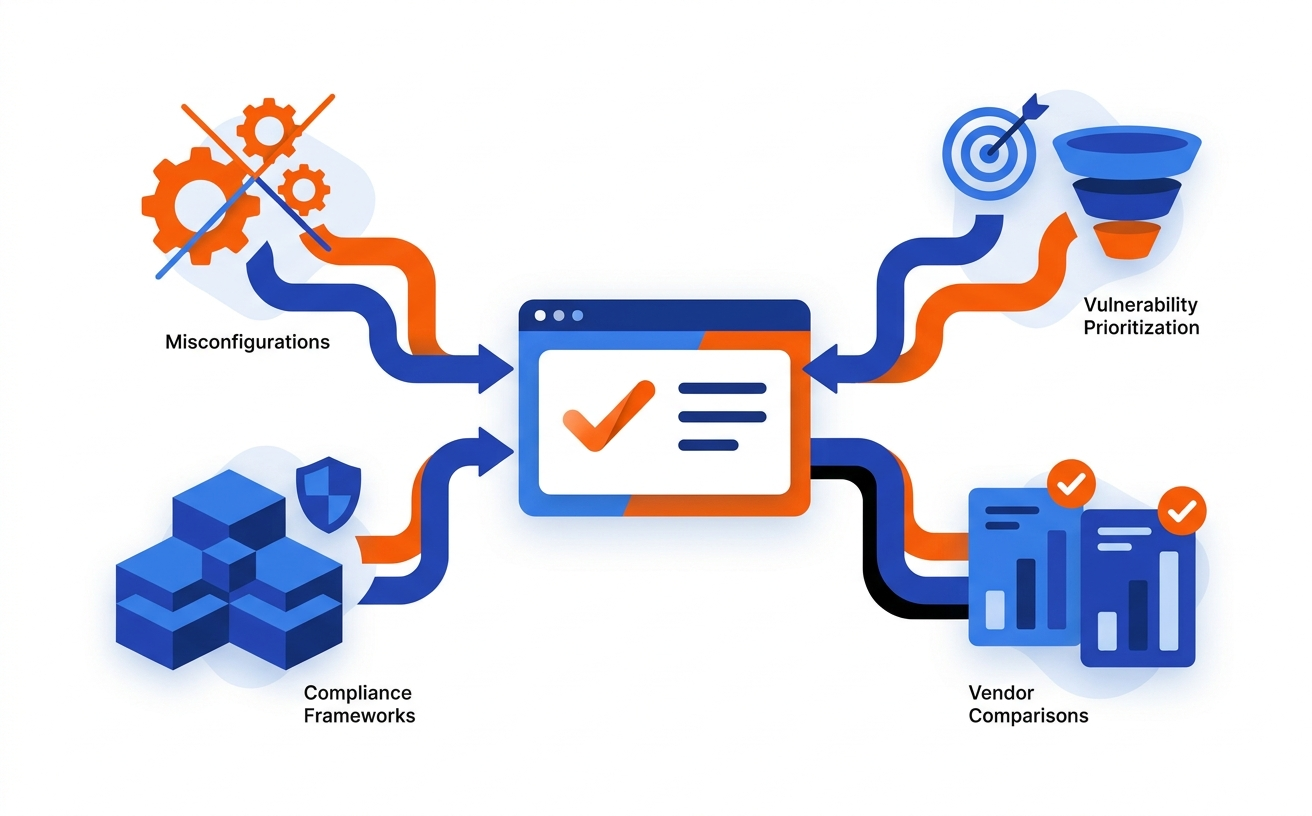
Our engagements are built around outcomes that move ARR, not outputs that look busy in a report.
A full audit of crawl architecture, Core Web Vitals, schema markup for SaaS product pages, and indexation health across your documentation and blog, so comparison and compliance pages can rank.
CSPM keyword research covering category terms, compliance-driven queries, cloud provider-specific terms for AWS, Azure and GCP misconfigurations, and bottom-of-funnel alternative searches.
Long-form guides, comparison pages, use-case landing pages and integration pages written by writers with cloud security fluency, plus programmatic templates for compliance frameworks and cloud provider integrations.
Digital PR and editorial placements in cybersecurity and cloud infrastructure publications that build domain authority with relevant audiences, even when legacy CSPM vendors hold page one.
Every deliverable is tracked against demo requests, trial sign-ups and pipeline contribution, not rankings alone.
The fastest onboarding on Earth. Your SEO program starts the day after you sign.
Goals, personas, competitors and priority pages.
Search Console, analytics, CMS and rank tracking connected.
Top technical and content fixes, ranked by pipeline impact.
Your first sprint starts on the pages closest to revenue.
| Novalab | Generalist agency | In-house hire | |
|---|---|---|---|
| Time to start | 24 hours | 2–4 weeks | 2–3 months to hire |
| Keywords mapped to CISO and cloud architect personas | ✓ | ✕ | Depends on hire |
| Technical, content and links in one team | ✓ | ✓ | ✕ |
| Google + AI search (GEO / AEO) | ✓ | Sometimes | Sometimes |
| Reporting tied to pipeline and MRR | ✓ | ✕ | Depends on hire |
Leads Novalab's SaaS SEO programs, from keyword strategy to pipeline reporting.
Can't find your answer? Ask us on a free strategy call.
Book a strategy callMost CSPM clients see measurable ranking improvements within 90 days on lower-competition and long-tail terms. Category-level keywords with strong incumbent rankings typically take six to nine months of consistent content production and link building. We set realistic timelines at the start of every engagement and share progress monthly.
We work with both. Early-stage companies benefit most from a content-first approach that builds topical authority in specific compliance niches or cloud environments before competing on broad category terms. Growth-stage vendors usually need technical fixes, content scale and programmatic SEO running in parallel to close the gap on established players.
Our team includes writers and strategists with backgrounds in cybersecurity and cloud infrastructure. We do not rely on freelancers who need a briefing document to understand what a security group misconfiguration means. That depth earns rankings and trust with technical buyers who will dismiss anything that reads like it was written from outside the industry.
Novalab runs SEO programs for CSPM and cloud security SaaS companies that want organic search to be a real revenue channel, not an afterthought. If your demo pipeline depends too heavily on paid ads and outbound, it is time to fix that. Contact the team and we will walk through your current search visibility, your biggest keyword opportunities, and what a 12-month organic program looks like for your growth targets.