Onboarding done in 24 hours
Kick-off, access, tracking and the first audit completed within 24 hours, so your API security platform starts winning search on day one.
See the 24h onboarding →
API security is a crowded, fast-moving market, and most vendors fill their demo calendars with paid ads. Security engineers and DevSecOps teams start their research on Google long before they book a call. If your content is not there when they search, a competitor's is, and your CAC keeps climbing.
Novalab builds organic search programs for API security vendors that generate qualified demo requests and trial starts, not just traffic. We map keywords to how security buyers actually research, produce technically credible content, and fix the site issues that hold rankings back. It is the same model we use as a SaaS SEO agency, applied to a technical niche.
Kick-off, access, tracking and the first audit completed within 24 hours, so your API security platform starts winning search on day one.
See the 24h onboarding →We write for security engineers and DevSecOps teams with real attack patterns, code-level detail and honest trade-offs, so content ranks and earns trust.
See the approach →Once a page ranks, each visitor costs close to nothing. That cuts your reliance on paid clicks that often run thirty to fifty dollars in this category.
See how →Most API security companies run the same playbook: paid search on a few high-intent keywords, conference sponsorships and SDR cold email. SEO sits at the bottom of the list because results are not immediate. That is exactly why it is an advantage for vendors willing to invest early. Your competitors are rarely doing it well, and the category has dozens of specific subtopics, from OWASP API Security Top 10 to BOLA, JWT vulnerabilities and mTLS. Adjacent demand exists too, such as SEO for attack surface management SaaS companies.
Buyers are technical and distrust marketing copy. They trust documentation, code examples, architecture diagrams and plain explanations of how things work. Content that reads like a brochure will neither rank nor convert in this niche.
Sales cycles are long and several people weigh in. An engineer finds your content, runs a trial and champions the tool, then a CISO or VP of Engineering signs off. Your SEO has to serve both audiences with different pages.
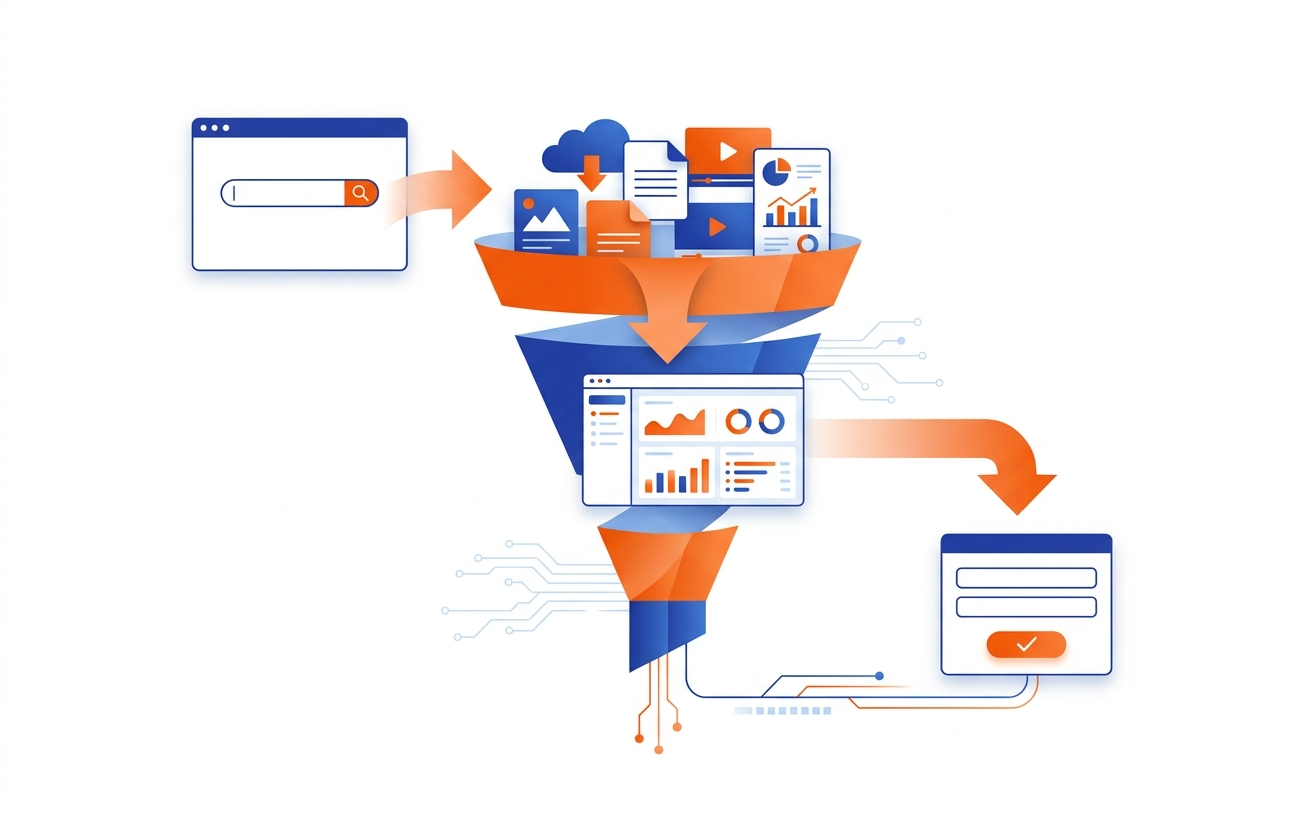
We start with keyword strategy for cloud security SaaS thinking applied to your category, covering all three funnel stages. Top-of-funnel queries like “API authentication best practices” attract developers who later become champions. Mid-funnel queries like “runtime API protection vs WAF” reach buyers shortlisting vendors. Bottom-funnel pages, such as integration-specific and industry use-case pages, link straight to demo or trial paths.
Content is the core of the work. We build deep technical explainers, vulnerability breakdowns, implementation guides and benchmark reports. A post on how BOLA attacks work and how to detect them in production pulls in a security engineer far better than a generic API security guide. Every piece gets a clear next step, such as a checklist, a technical guide or a demo CTA.
Technical depth also signals expertise to Google. That means citing specific RFCs, referencing real attack patterns from recent breach reports and explaining implementation trade-offs precisely. Thin content does not rank in this space. Genuine expertise does.
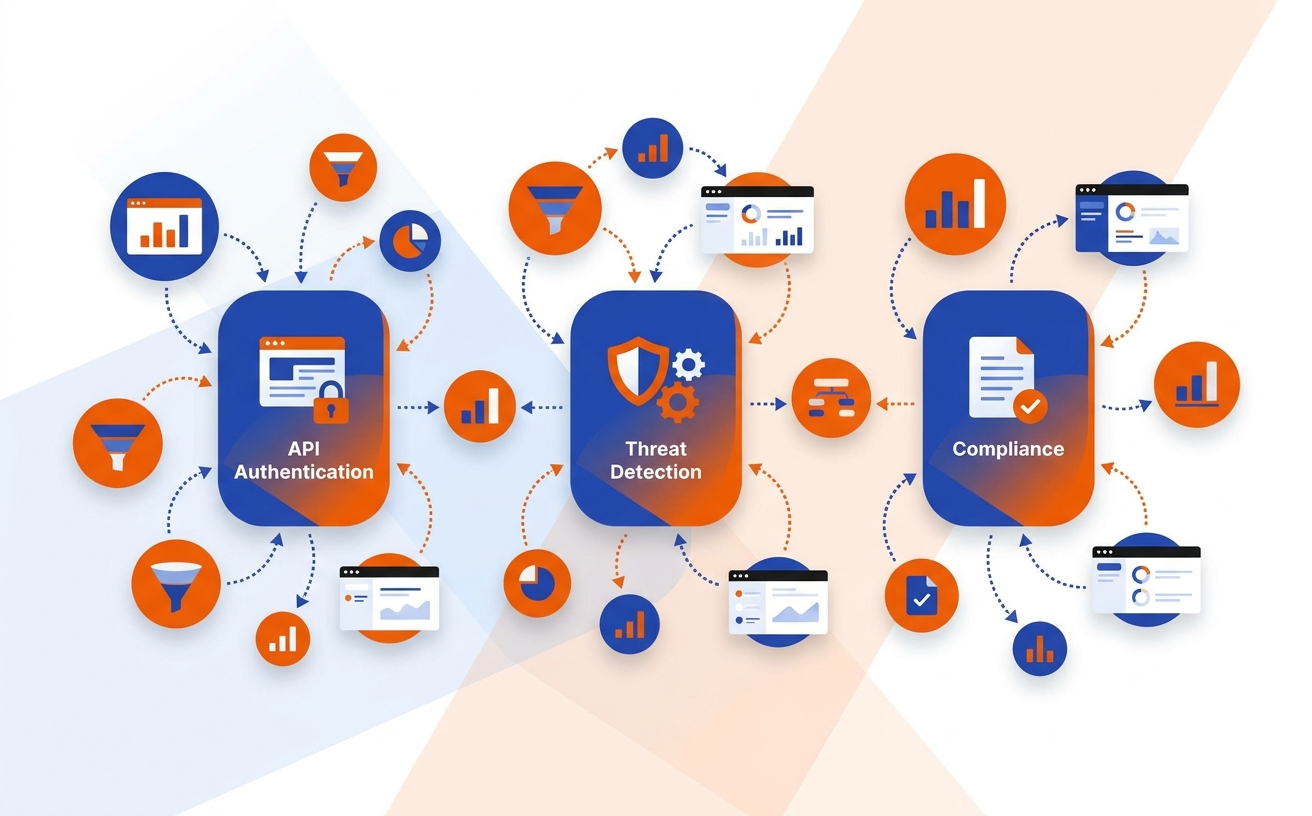
Strong content needs a site that supports it. We separate product pages, solution pages and blog content and link them with intent. Each major theme, such as API authentication, API threat detection and API compliance, gets one authoritative pillar page with cluster posts linking back to it. Our SaaS SEO audit checklist shows the kind of issues we look for.
We also make sure your documentation subdomain or developer portal does not compete with or cannibalize your main site rankings. We add schema markup to FAQ sections and how-to guides to win rich results in crowded SERPs.
Core Web Vitals matter too. SaaS sites with heavy marketing stacks often carry performance debt that suppresses rankings, and fixing it removes a drag on every page you publish.
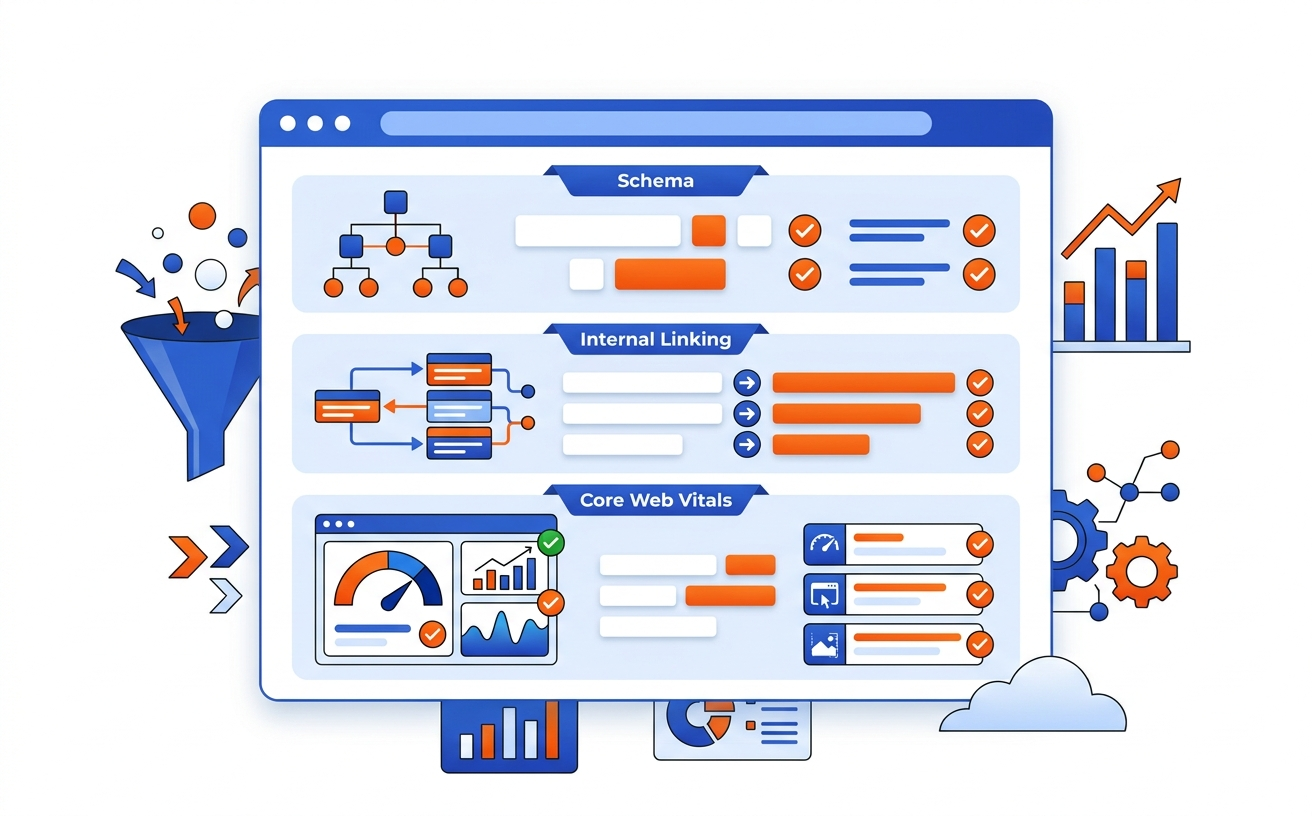
Every engagement covers the work that turns technical search demand into demos and trials.
Site architecture, topic clusters, schema markup, Core Web Vitals fixes and docs-versus-marketing-site separation so your rankings are not held back.
A funnel-wide keyword map covering security engineer research queries, vendor comparison terms and high-intent pages like API security for AWS API Gateway.
Technical explainers, vulnerability breakdowns, implementation guides and comparison pages written with the depth security buyers expect, each with a clear conversion path.
Link and mention building from credible security and developer sources that reinforces the expertise your content already shows.
All of it is reported against demo requests, trial starts and CAC, not vanity traffic.
The fastest onboarding on Earth. Your SEO program starts the day after you sign.
Goals, personas, competitors and priority pages.
Search Console, analytics, CMS and rank tracking connected.
Top technical and content fixes, ranked by pipeline impact.
Your first sprint starts on the pages closest to revenue.
| Novalab | Generalist agency | In-house hire | |
|---|---|---|---|
| Time to start | 24 hours | 2–4 weeks | 2–3 months to hire |
| Keywords mapped to security engineer personas | ✓ | ✕ | Depends on hire |
| Technical, content and links in one team | ✓ | ✓ | ✕ |
| Google + AI search (GEO / AEO) | ✓ | Sometimes | Sometimes |
| Reporting tied to pipeline and MRR | ✓ | ✕ | Depends on hire |
Leads Novalab's SaaS SEO programs, from keyword strategy to pipeline reporting.
Can't find your answer? Ask us on a free strategy call.
Book a strategy callExpect meaningful organic traffic growth within four to six months of consistent content and technical work. Demo requests and trial starts from organic search usually become measurable between six and twelve months. The timeline depends on your domain authority, content volume and keyword competition. API security is a focused category, which can make it faster to rank than broader software niches.
Both. Security engineers and DevSecOps professionals research tools, run trials and champion a purchase internally. CISOs, VPs of Engineering and procurement leads validate it. Aim top-of-funnel content at practitioners and solution and ROI pages at business stakeholders. For related niches, see our approach to SEO for penetration testing platform SaaS companies.
Paid search is faster but expensive. CPCs for cybersecurity and API-related keywords often exceed thirty to fifty dollars per click, and security buyers rarely convert on a first visit. SEO builds an asset that compounds without ongoing spend. The strongest setup combines paid for immediate pipeline with SEO for long-term growth, since paid-only growth stops the moment spend stops.
Novalab works with technical SaaS companies to build SEO programs that produce real pipeline, not just traffic. We handle keyword strategy, content, technical SEO and reporting so your team can stay focused on the product. If you want to cut your dependence on paid acquisition, contact us for a free strategy call.