Onboarding done in 24 hours
Kick-off, access, tracking and the first audit completed within 24 hours, so your penetration testing platform starts winning search on day one.
See the 24h onboarding →
Penetration testing platforms sell into one of the most competitive and trust-sensitive corners of SaaS. CISOs, security engineers, and procurement teams research for weeks before they book a demo. If your platform is not on page one when they search, a competitor collects that pipeline.
Novalab builds organic search programs that put penetration testing SaaS companies in front of the right decision-makers at the right moment in the buying cycle. A SaaS SEO agency that treats red-team leads like generic B2B buyers will keep targeting the wrong DAST and continuous-pentesting keywords. We map content to how security buyers actually research and compare platforms.
Kick-off, access, tracking and the first audit completed within 24 hours, so your penetration testing platform starts winning search on day one.
See the 24h onboarding →We map keywords to each stage of a long security sales cycle, from awareness queries about vulnerability management to bottom-of-funnel platform comparisons.
See the approach →High-intent security keywords often cost over two hundred dollars per click. Organic pages keep generating demo requests months after launch without added spend.
See how →Most SEO agencies do not understand the difference between a DAST tool and a continuous pentesting platform. That gap shows in the content they produce, the keywords they target, and the backlink sources they chase. Security buyers spot shallow content immediately, and shallow content does not convert. SEO consulting for SaaS scopes the pentesting buyer intent map before generic backlinks land on the wrong pages.
The sales cycle is also longer. A prospect might read your blog in January, attend a webinar in March, and request a trial in June. Organic search has to support every stage of that journey, which is why we map keyword clusters from awareness-level queries about vulnerability management to comparisons between specific platforms.
Technical requirements are more demanding too. Security platforms often serve content behind authentication, deal with compliance-related indexing concerns, and need schema markup that signals authority to both Google and cautious buyers. We handle that layer before comparison pages start ranking.
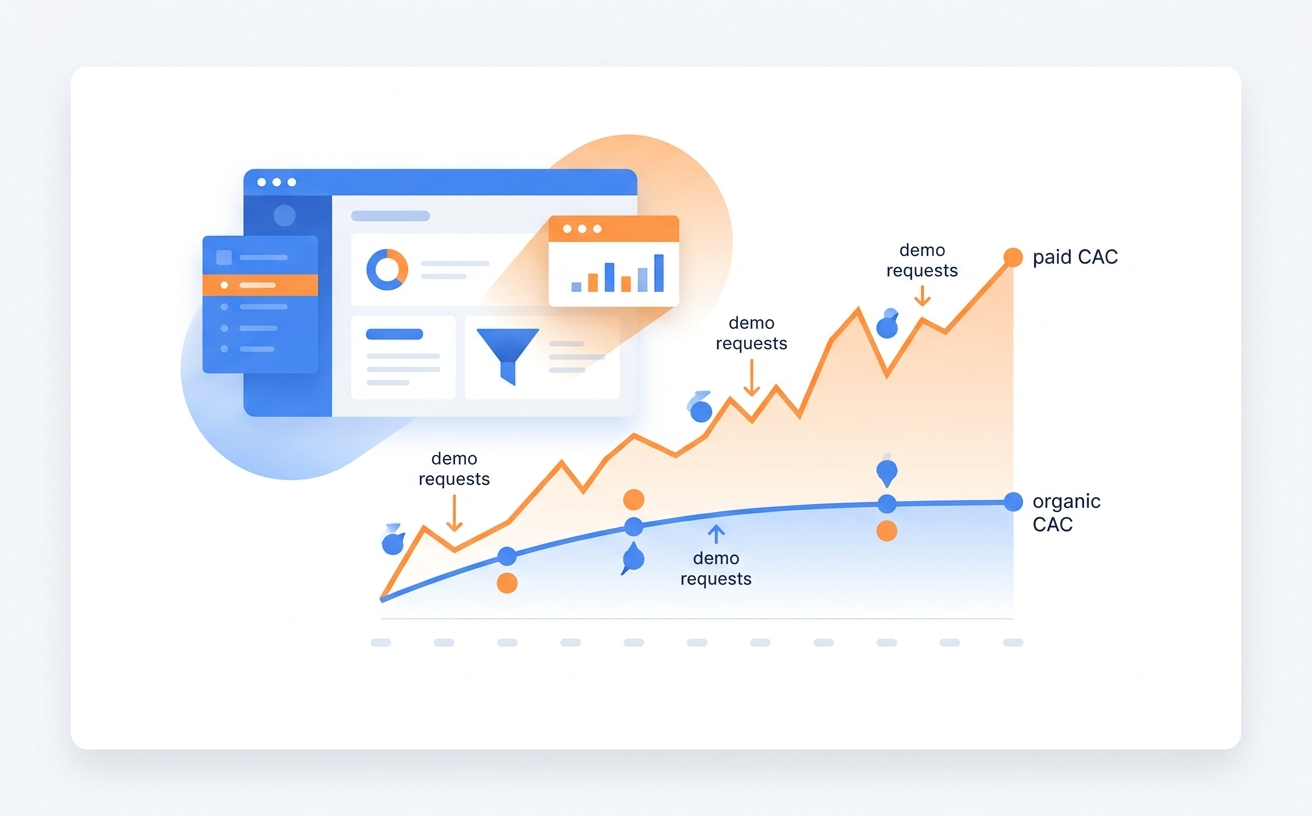
Paid acquisition in cybersecurity is expensive. Cost-per-click for high-intent security keywords regularly exceeds two hundred dollars, so companies that rely only on paid channels watch CAC climb as they scale. Organic search compounds. A well-optimized page written today keeps generating demo requests twelve months from now without additional spend. Our SEO for cybersecurity SaaS companies work covers the enterprise-security research path when buyers evaluate several security categories at once.
For penetration testing platforms, the highest-value pages tend to be product comparison pages, use-case pages for verticals like fintech or healthcare, and technical guides that attract links from security researchers. We identify which of these will move the needle fastest for your ICP and build them in order of expected return.
As organic traffic grows, companies typically see trial signups increase without proportional growth in marketing spend. That improves MRR efficiency and takes pressure off paid channels. Inbound leads also arrive further along, because they have already educated themselves on your content.
Penetration testing buyers rarely evaluate in isolation. They compare vulnerability tooling, external exposure tools, and cloud security products in the same research sessions. SEO for attack surface management SaaS companies follows the external-exposure and asset-discovery research path that overlaps with pentesting evaluations, and we use the same logic to place your platform in those comparisons.
The same applies to cloud and orchestration queries. When a buyer connects pentesting findings to cloud misconfiguration review or automated response workflows, they search for terms outside the core pentesting vocabulary. We map those adjacent clusters so your platform appears across the full evaluation, not only on the obvious head terms.
Early-stage companies benefit from building topical authority quickly and capturing long-tail keywords before larger vendors dominate them. Established platforms benefit from closing competitor gaps, improving conversion on existing organic traffic, and expanding into adjacent clusters that feed ARR growth from new market segments.
Our engagement covers the full organic growth stack, built for security buyers who read carefully and convert slowly.
A technical audit surfaces crawl issues, Core Web Vitals failures, and indexation problems quietly suppressing rankings, including those caused by authentication-heavy security sites. We fix them with <a href="https://thenovalab.com/technical-seo-for-saas/">technical SEO for SaaS</a> before content scales.
We anchor the strategy to real commercial intent, not vanity traffic. Red-team, DAST, and compliance-framework terms are mapped to each funnel stage through <a href="https://thenovalab.com/keyword-research-services/">keyword research services</a>.
Our writers have cybersecurity and B2B SaaS backgrounds, so they write accurately about network penetration testing, red team workflows, CVE scoring, and frameworks like SOC 2 and ISO 27001.
Digital PR and link acquisition from security media builds authority where legacy pentesting vendors hold page one, supported by <a href="https://thenovalab.com/saas-link-building/">SaaS link building</a>.
Monthly reporting ties every deliverable to demo requests, pipeline, and CAC, so you can see what organic search contributes to ARR.
The fastest onboarding on Earth. Your SEO program starts the day after you sign.
Goals, personas, competitors and priority pages.
Search Console, analytics, CMS and rank tracking connected.
Top technical and content fixes, ranked by pipeline impact.
Your first sprint starts on the pages closest to revenue.
| Novalab | Generalist agency | In-house hire | |
|---|---|---|---|
| Time to start | 24 hours | 2–4 weeks | 2–3 months to hire |
| Keywords mapped to security buyer personas | ✓ | ✕ | Depends on hire |
| Technical, content and links in one team | ✓ | ✓ | ✕ |
| Google + AI search (GEO / AEO) | ✓ | Sometimes | Sometimes |
| Reporting tied to pipeline and MRR | ✓ | ✕ | Depends on hire |
Leads Novalab's SaaS SEO programs, from keyword strategy to pipeline reporting.
Can't find your answer? Ask us on a free strategy call.
Book a strategy callMost clients see meaningful ranking improvements within three to five months. Pipeline impact from organic typically becomes measurable between months four and seven, depending on domain authority at the start. Penetration testing is a high-intent category, so even modest gains on commercial keywords can produce significant demo volume.
Yes. Our content team includes writers with hands-on cybersecurity backgrounds. We add a structured briefing that captures your differentiators, your ICP, and any proprietary methodologies you want featured. The result reads like it came from inside your organization without consuming your engineering team’s hours. The same standard applies to SEO for security awareness training SaaS companies, where security-culture content has to be equally credible.
We work with both. Early-stage companies benefit from building topical authority quickly and capturing long-tail keywords before larger competitors own them. Established platforms benefit from closing competitor gaps, lifting conversion on existing organic traffic, and expanding into adjacent keyword clusters that add ARR from new segments.
Novalab specializes in SEO for security-focused SaaS companies. We understand your buyers, your compliance environment, and the content standards your audience expects. If you want more demo requests from organic search without inflating your CAC, our team is ready to build the program. Contact us today to request a strategy call and a no-cost keyword opportunity analysis for your penetration testing platform.